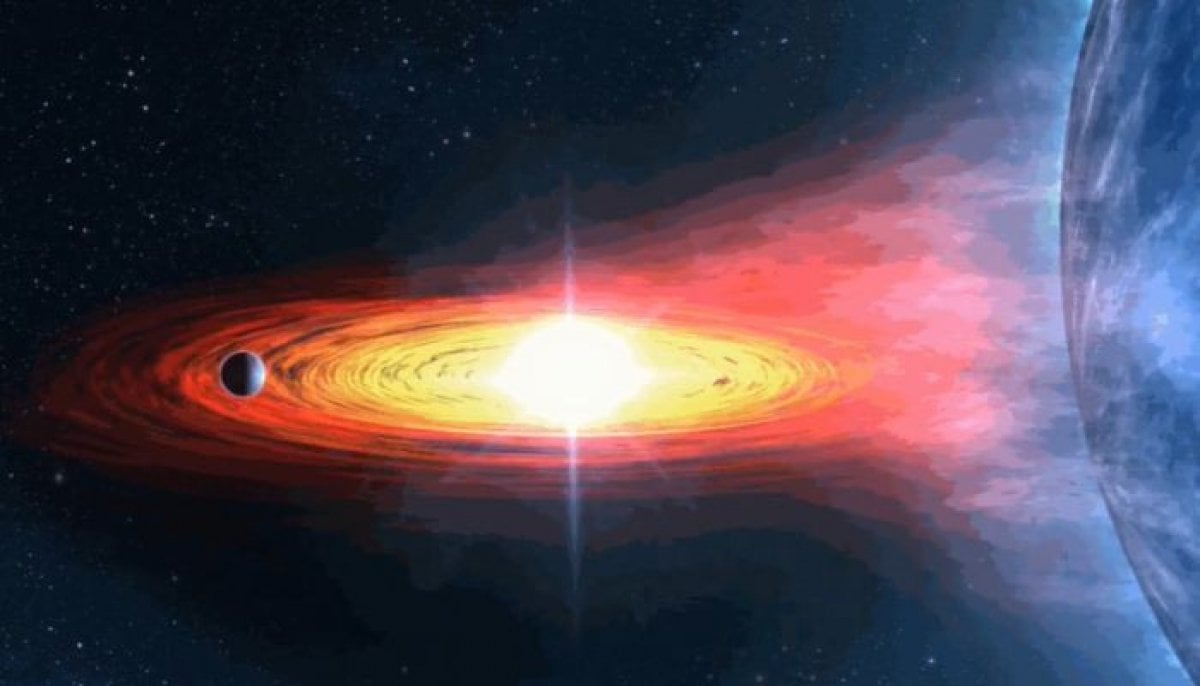
Radio signals coming directly from an exoplanet, a planet outside the solar system, have been detected for the very first time.
Scientists from the University of Chicago used climate models to predict the impact the devastating climate event could have.
A flaw in cPanel's CalDAV and CardDAV service lets anyone with a cPanel hosting account run code as root and take "full control of the server," the company said on September 22. A second bug in the WP Toolkit plugin, used to install and manage WordPress sites, allows an account holder to change databases that belong to other accounts. cPanel has released fixed versions for both,
Ukraine will get access to OpenAI's advanced GPT 5.6 Sol model under the deal - a rival to Anthropic's Mythos and Fable
Autonomous security agents are getting good at finding bugs. Nobody has a good way to measure how good. Point one at a realistic target and what comes back is a report the agent wrote about itself: confident prose, a list of findings, and no way to tell which of them happened. Someone with a security background then sits down and checks every claim against the target. Which findings are real,
Anthropic and OpenAI on Tuesday announced new models, with both artificial intelligence (AI) companies noting that they are continuing to invest in improving alignment to combat risky behavior. Opus 5.5, per Anthropic, is a "major step up from Opus 5," and "achieves the best scores of any model to date on our automated behavioral audit, our alignment suite that tests Claude across thousands
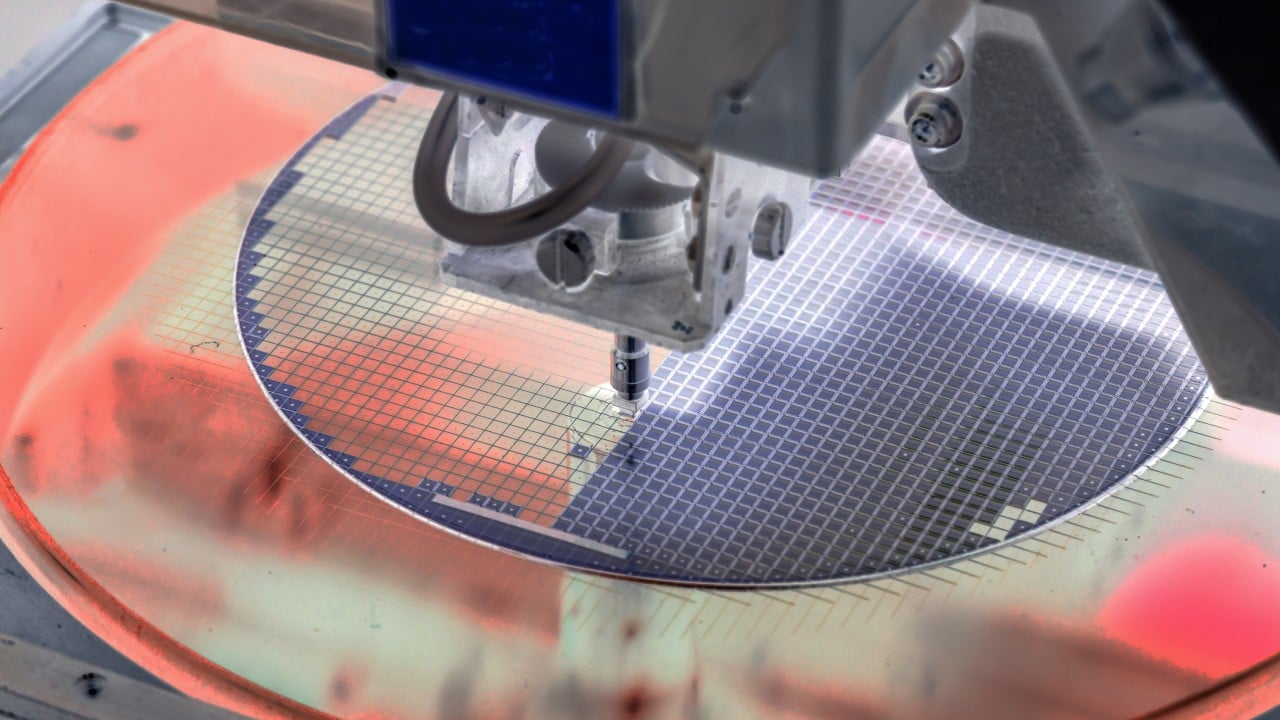
Chinese storage makers, long known for packaging chips into modules, have been moving up the value chain into wafer-level operations, with the latest firm to make the jump investing 4.5 billion yuan (US$672 million) in an advanced packaging project. The sum, which Shanghai-listed Biwin Storage Technology will pour into the third phase of its advanced packaging and testing project in Dongguan, in southern China’s Guangdong province, will exceed the 3.09 billion yuan it put into the first two...
A use-after-free in the Linux kernel's AF_UNIX socket subsystem can be used to escape a container and gain root on the host, security firm DepthFirst said in research published September 22. The flaw, tracked as CVE-2026-80521 (CVSS score: 7.8), was fixed upstream on August 6, but Ubuntu has not shipped the patch for its 26.04, 24.04, or 22.04 LTS releases. DepthFirst
First-ever radio signal from exoplanet reveals its magnetic field Astronomers in a recent breakthrough have captured a strange radio signal coming from a distant planet outside the solar system for the first time. According to the researchers from the Harvard-Smithsonian Centre for...
ShinyHunters claims it breached the FBI and stole sensitive data belonging to agents and job applicants. The hacker group says it accessed terabytes of information through an Oracle PeopleSoft server and an Amazon-hosted government cloud.
Farmers fear they may not be able to carry out environmental work because they lost out on funding.
Oppo Find X10 Pro Max launched in China with triple 200MP cameras, an 8,000mAh battery, the Dimensity 9600 Pro chipset, and a 6.78-inch 144Hz display. India launch expected around Diwali/end-October 2026; local pricing not announced.
Attackers are exploiting a critical flaw in F5 BIG-IP Access Policy Manager (APM) that lets them run code on a BIG-IP system without logging in, F5 says. The flaw, CVE-2026-94127, affects only systems in which APM serves as an OAuth authorization server, issuing access tokens to applications. F5 disclosed it in an advisory on September 22 and has released engineering hotfixes.